The proposal includes a unique code on every bottle and a page that says genuine after scanning. The buyer describes it as anti-counterfeit packaging. Before that claim enters the artwork, the team needs to ask what the system actually verifies and how it distinguishes an authorized physical item from a copied code.
Define the claim and evidence before ordering serialized labels. Unique numbering, destination access, authenticity assessment and tamper evidence are different functions. A scan result should communicate only the conclusion the supported system can establish.
Separate identity from authentication
A serial number can distinguish an intended record from another record. Its presence does not, by itself, show that the physical package carrying it is the authorized item. Ask the system provider which data and physical features support the intended conclusion.
GS1's digital-signature guidance discusses signatures, serialized identifiers and additional physical security factors as parts of a broader approach. It does not turn every printed unique QR code into an authenticated product.
Keep the label supplier's production role separate from the system provider's security claims. A printer may be able to produce and reconcile variable codes without providing an authentication service. Obtain confirmation of the actual scope each party accepts.
Write the intended scan statement first
Ask what a consumer or operator should learn: the code exists in an authorized database, the item has a particular record, the scan is suspicious or another specific conclusion. Have the responsible brand and security owners review the wording.
Avoid an unconditional genuine message when the system only confirms that a code is recognized. Explain the limits through the approved user experience. Do not add an unsupported guarantee to the physical label because the backend uses a security-sounding product name.
The general QR guide addresses code use and layout. Authentication procurement needs a separate claim-and-evidence decision behind that physical symbol.
Use a claim-to-evidence matrix
| Proposed claim | Question for the provider |
|---|---|
| Unique code | How are records created and unintended duplicates controlled? |
| Authorized origin | What links the record to authorized manufacture and the physical item? |
| Duplicate detection | What observations trigger review, with what limitations? |
| Tamper indication | Which physical feature reveals the intended opening or alteration? |
| Consumer response | What does each scan message actually mean? |
| Offline/failure state | What happens when service or connectivity is unavailable? |
| Investigation | Who receives an alert and decides the next action? |
| Lifecycle | How are returns, replacements, retired codes and service changes handled? |
This is an editorial procurement matrix, not a security certification or attack assessment. The system provider and responsible specialists must substantiate the actual claims.
Connect printing control with system control
Define the approved data file or generation interface, record ranges and reconciliation method. Ask how rejected, unused and replacement labels are handled. A secure backend still needs a controlled physical printing and application process.
The serialized-label reconciliation guide addresses rejected and replacement records. That work supports data integrity, while the authentication decision asks what those records prove about a physical item.
Keep test codes clearly separated from production records. Do not let photography samples or proof files create loose production identities that later enter the supply chain without the agreed controls.
Review the physical feature in its actual role
If a label is intended to bridge an opening or reveal interference, define the physical event and the observation expected. A serialized front label may remain untouched when a cap is opened. Its uniqueness does not create tamper evidence at another part of the package.
The food-seal guide maps an opening path before selecting a strip. Keep that review linked to the security proposal while avoiding a claim that one simple seal prevents every form of interference.
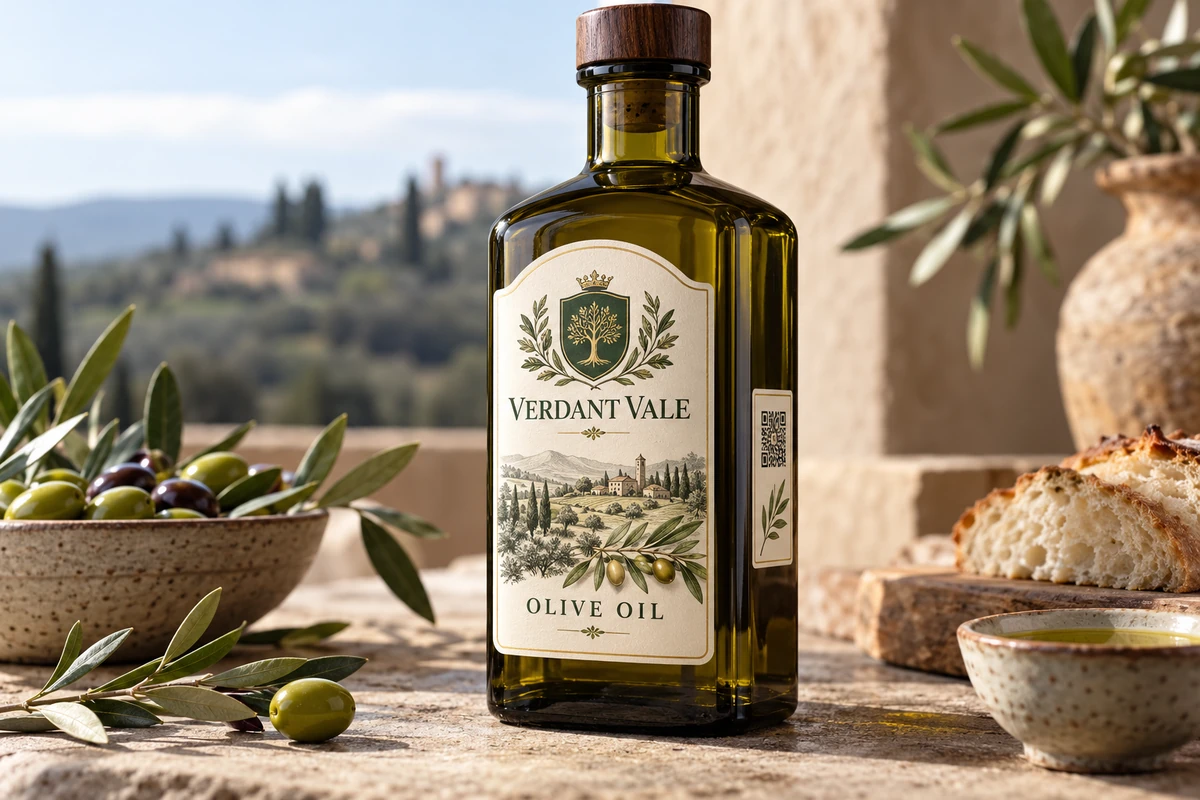
For a hypothetical premium oil bottle, the brand might want both item identification and an opening indicator. Those are two requirements that may be addressed by different components and evidence. Approve each explicitly.
Ask how the service handles ambiguous results
Connectivity failure, an unreadable symbol, a previously scanned item or a returned product can create different situations. The provider should explain the supported behavior and the limits of any suspicious-activity inference. A repeated scan alone may have several ordinary explanations.
The business also needs an escalation owner. A consumer warning with no investigation or support route can create confusion rather than a usable control. Confirm who reviews the event and what information is available under the actual service and privacy arrangements.
Do not publish operational security details unnecessarily in consumer artwork. Keep sensitive configuration and access information in the business's approved systems while making the customer-facing statement accurate.
Require a claim owner at the service boundary
Ask who is authorized to approve the statement shown after a scan and who maintains that statement when the service changes. A printer should not copy a security claim from a demonstration screen into consumer artwork without that approval. Keep the supported message and the actual service version in the release record.
Release the claim with its limitations understood
Keep the approved scan wording, system scope, physical-label specification and production reconciliation requirements together. Review the claim when the provider, code format, packaging or service lifecycle changes.
A successful demonstration can support the specific function shown. It should not be reported as proof of resistance to every counterfeit method or as a measured reduction in counterfeit products without relevant evidence.
Discuss a serialized-label production brief with the intended identifier format, data-control requirements, physical label role and the system provider's confirmed scope. Mark authentication questions for the responsible specialist. The form opens an email draft; review it and attach permitted requirements through email or the listed WhatsApp route.